Compliance that lives in your code, not a binder.
DPDP compliance services that build the Act into your product
India’s Digital Personal Data Protection Act applies to any organization processing the personal data of people in India, regardless of where the company is based. We help engineering and product teams turn its obligations — consent, data rights, breach response — into working systems, not a policy document that doesn’t match what the product actually does.
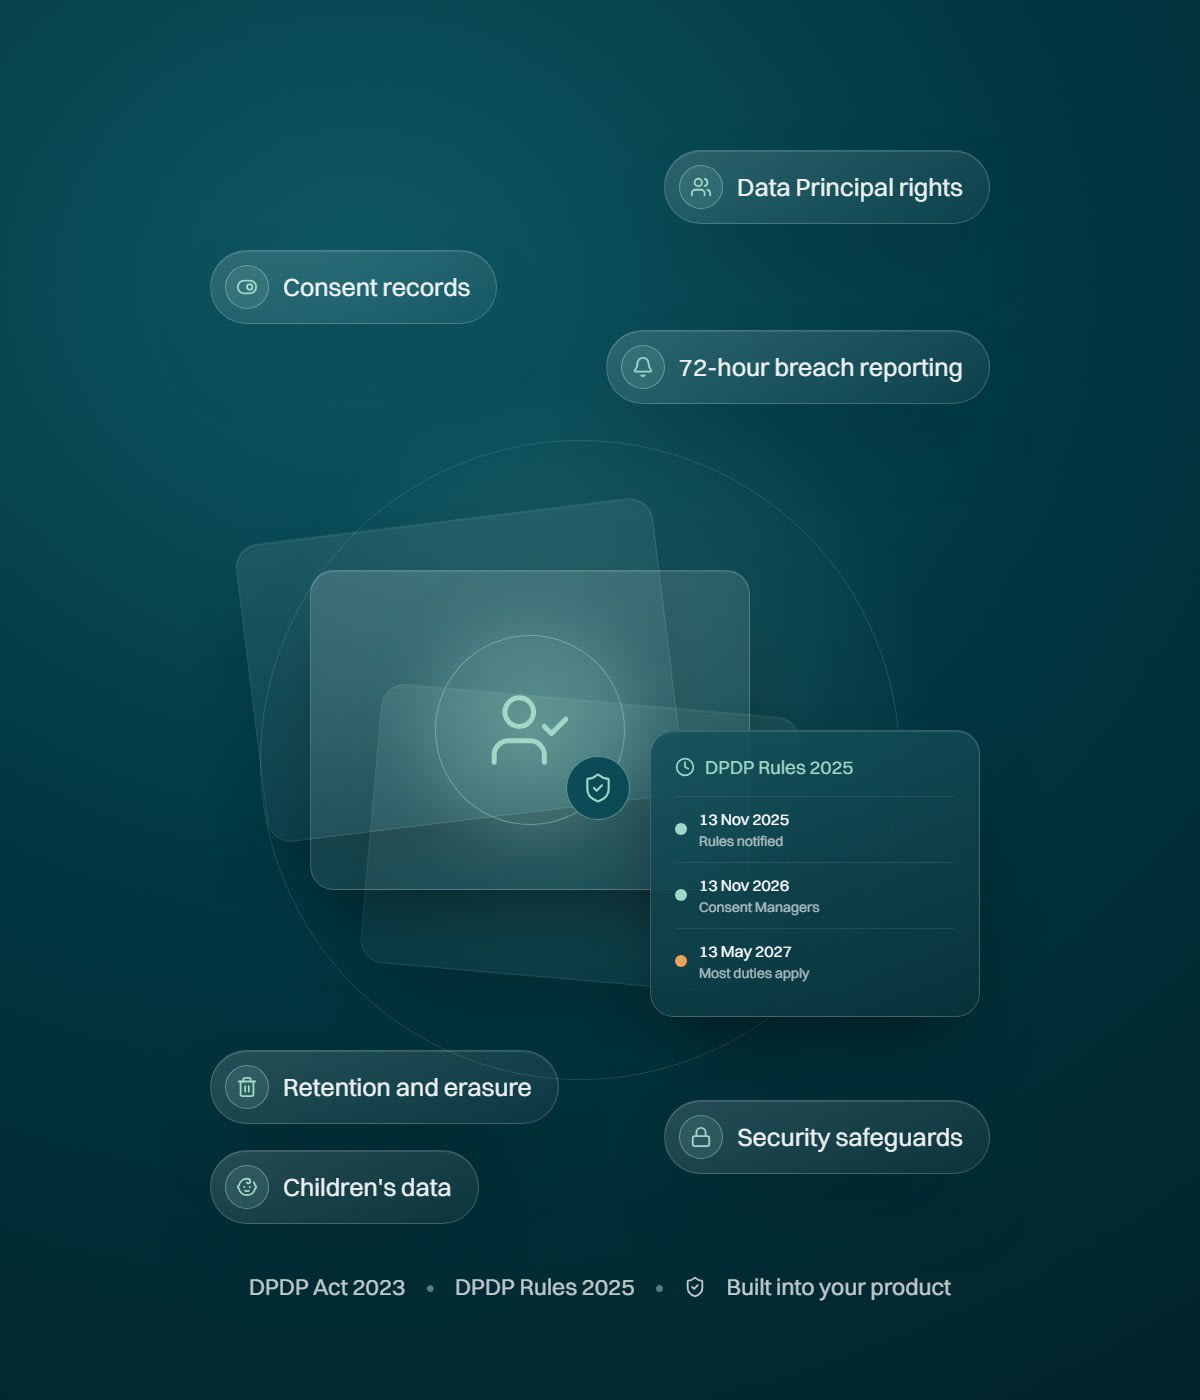
DPDP compliance in India means meeting the Digital Personal Data Protection Act, 2023 and the DPDP Rules, 2025 in how your product actually collects, uses, stores and deletes personal data. Tizora's DPDP compliance services design and build the consent flows, rights-request systems, retention jobs and breach reporting that make it true in practice, alongside your legal counsel.
This page explains engineering work and is not legal advice.
DPDP Rules 2025: the DPDP compliance deadline timeline
| Date | What applies |
|---|---|
| 11 Aug 2023 | Digital Personal Data Protection Act, 2023 enacted. |
| 13 Nov 2025 | DPDP Rules, 2025 notified. Rules setting up the Data Protection Board take effect immediately. |
| 13 Nov 2026 | Registration and obligations of Consent Managers (Rule 4). |
| 13 May 2027 | Most duties for Data Fiduciaries: notice, security safeguards, breach intimation, retention and erasure, children's data, Significant Data Fiduciary obligations, Data Principal rights and transfers outside India (Rules 3 and 5 to 16). |
The time to build consent records, rights flows and breach reporting is before May 2027, not after it.
What DPDP Act compliance requires of your product
The Digital Personal Data Protection Act, 2023 is built around two roles: the Data Fiduciary (the organization deciding how and why data is processed) and the Data Principal (the individual the data belongs to). Every obligation in the Act — clear notice, purpose limitation, data minimization, timely breach reporting, and honoring a Data Principal’s rights — has to be true of your actual system at the moment a user interacts with it, not just true on paper. The DPDP Rules, 2025 add the operational detail, including notice content, security safeguards, breach timelines and how rights requests must be handled. That’s the gap most DPDP Act compliance programs run into: a privacy policy can promise data minimization, but only the engineering behind data collection forms, retention jobs, and access-request handling can actually deliver it. We work at that layer.
- Location
- Remote-first, global engagements
- Service
- DPDP compliance services
- Cooperation period
- Readiness review or ongoing compliance support
- Services used
- Consent architecture · Rights fulfillment systems · Breach response design · DPO advisory support
DPDP compliance checklist for product and engineering teams
Use this DPDP compliance checklist to see what your product must do before most duties apply on 13 May 2027. Each item is something your systems have to do, not just something your policy says.
Notice and consent
- Map every piece of personal data you collect: why, where it flows and who can access it.
- Show a standalone, itemized notice at collection that names each purpose (Rule 3).
- Record consent for each purpose, and make withdrawing consent as easy as giving it.
- Get verifiable parental consent before processing the personal data of anyone under 18 (Rule 10).
Data Principal rights
- Give people working flows to access, correct, update and erase their data, and to nominate someone to act for them.
- Publish a contact for your Data Protection Officer or designated officer, and answer requests and grievances within 90 days (Rule 14).
Retention, security and breaches
- Delete personal data once its purpose is complete, including in backups, replicas and analytics tables (Rule 8).
- Apply reasonable security safeguards such as encryption, masking and role-based access (Rule 6).
- Keep security logs for at least one year (Rule 6).
- Detect breaches, tell affected people and the Board without delay, and send the Board a detailed report within 72 hours (Rule 7).
Governance
- Check every transfer of personal data outside India against any country the government restricts.
- If you may be a Significant Data Fiduciary, plan for an India-based DPO, independent data audits and data protection impact assessments.
This checklist explains engineering work and is not legal advice. Confirm how each item applies to you with your legal counsel or DPO.
Check your product against this list with a DPDP readiness reviewDPDP compliance is a product and engineering problem, not just a legal one.
DPDP compliance software vs a policy rewrite vs building it into your product
| Question | Policy rewrite only | DPDP compliance software (consent tools) | Tizora: built into your product |
|---|---|---|---|
| What you get | An updated privacy notice and policy | A consent banner, consent records and a request portal | Consent, rights, retention and breach controls inside your own systems |
| Consent | Described in the policy | Captured at the front end | Captured per purpose and enforced in the backend and database |
| Rights requests | Usually an email address | A request form and tracking | Requests that actually find, correct and delete the data |
| Deletion across systems | Not covered | Depends on your integrations | Reaches backups, replicas and analytics tables |
| 72-hour breach report | A written procedure | Rarely covered | Detection, escalation and a reporting runbook |
| Works with the others? | Yes | Yes | Yes. We can connect your product to a consent tool or registered Consent Manager |
The obligations we help you operationalize.
Organized around the three relationships the Act actually governs: the individual, the organization, and the regulator. If AI features in your product handle personal data, pair this with an AI security assessment.
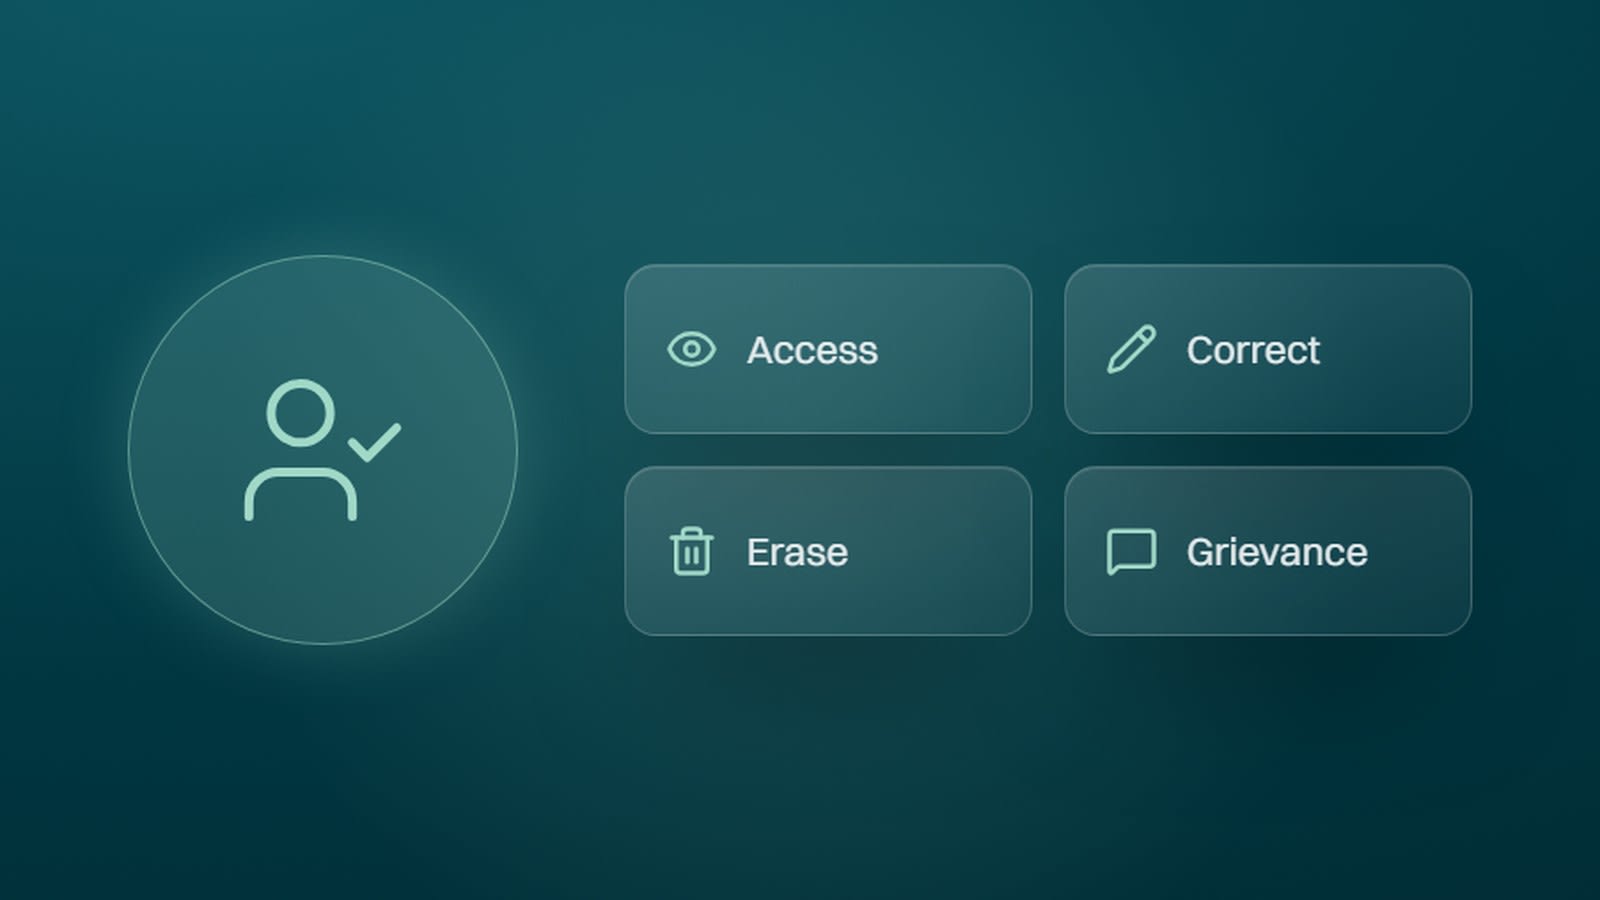
Data Principal side
- Clear, itemized notice at collection
- Right to access & correction
- Right to erasure & withdrawal of consent
- Nomination & grievance redressal
- Grievances answered within a published period of no more than 90 days (Rule 14)
Data Principal side
What individuals can see and ask for: itemized notice at collection, access and correction, erasure and withdrawal of consent, and nomination and grievance redressal.
We check that each right can actually be exercised in your product.
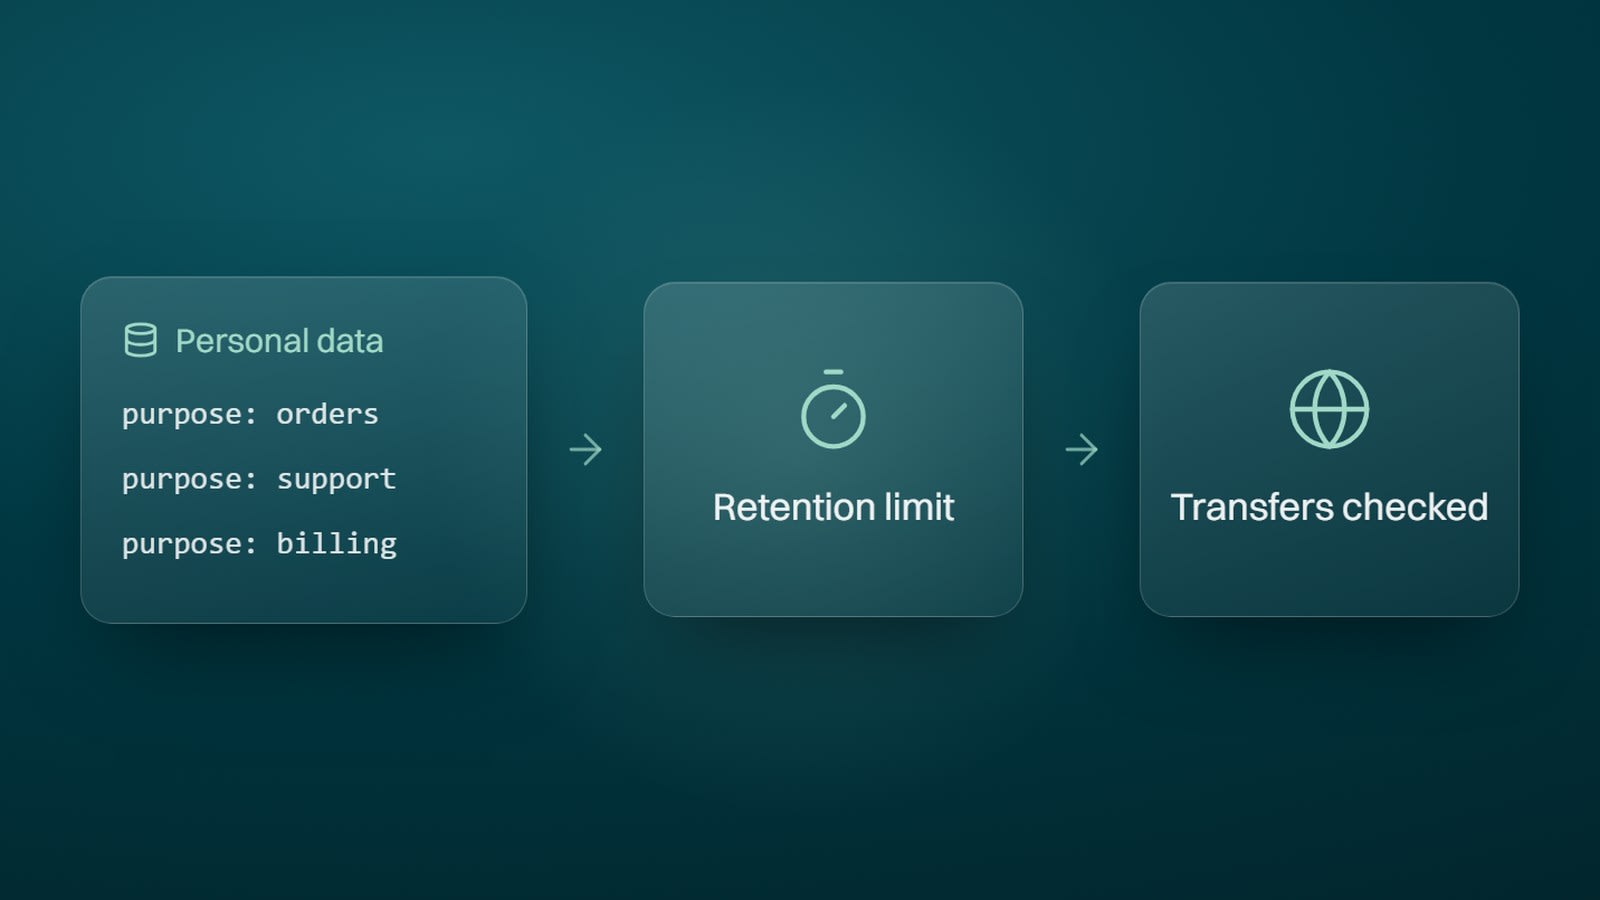
Data Fiduciary side
- Purpose limitation & data minimization
- Retention limits & deletion on purpose completion
- Children’s data & parental consent handling
- Cross-border transfer restrictions
- Security logs kept for at least one year (Rule 6)
Data Fiduciary side
What your organization owes: purpose limitation, data minimization, retention limits and deletion, children's data and parental consent, and cross-border transfer rules.
We map these obligations to how your systems handle personal data.
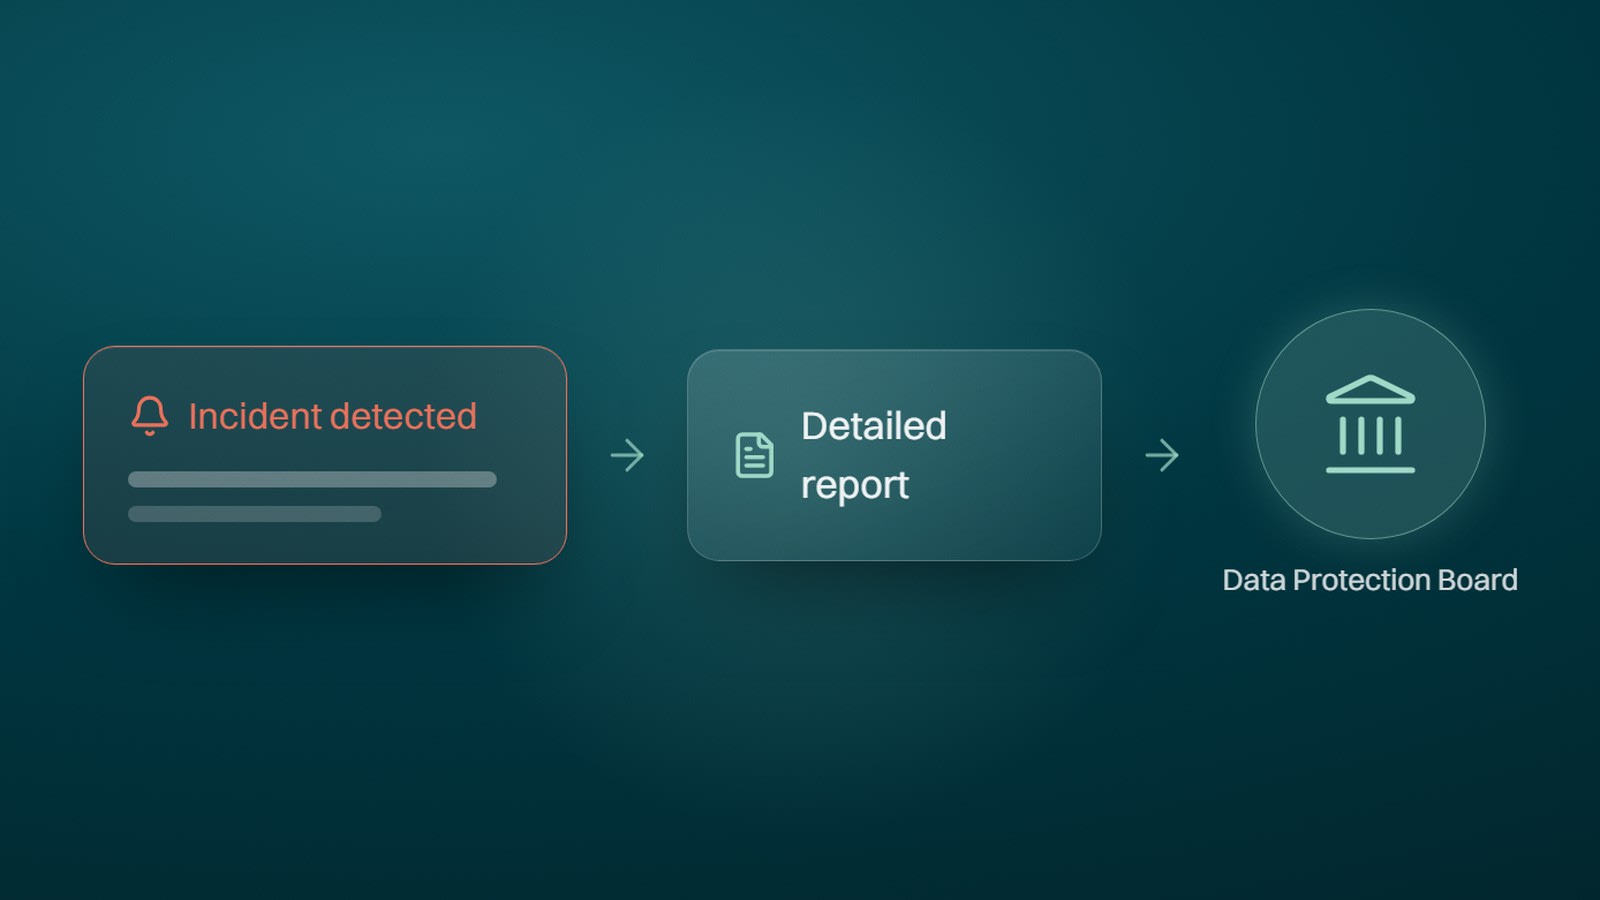
Regulator & incident side
- Data Protection Board reporting
- Personal data breach notification
- Significant Data Fiduciary obligations
- Data protection impact assessments
- Detailed breach report to the Board within 72 hours (Rule 7)
Regulator & incident side
How you report and respond: Data Protection Board reporting, breach notification, Significant Data Fiduciary obligations and impact assessments.
We review that the process is in place before it is needed.
DPDP Act penalties
| Failure by a Data Fiduciary | Penalty, up to |
|---|---|
| Not taking reasonable security safeguards to prevent a personal data breach | ₹ 250 crore |
| Not notifying the Board or affected individuals of a personal data breach | ₹ 200 crore |
| Not meeting obligations for children's personal data | ₹ 200 crore |
| Any other violation of the Act or Rules | ₹ 50 crore |
The Data Protection Board decides the amount, based on factors such as the nature, gravity and duration of the breach.
DPDP compliance solutions our services cover
Where engineering ends and legal advice begins
| Tizora (engineering) | Your legal counsel or DPO |
|---|---|
| Data mapping of what personal data is collected, where it flows and who can access it | Interpreting how the Act applies to your business |
| Consent flows and consent records in the product | Privacy notice and policy wording |
| Rights-request, retention and deletion systems | Contracts with processors and partners |
| Breach detection, escalation and reporting pipeline | Representing you before the Data Protection Board |
| Technical documentation, data maps and runbooks | Final sign-off on compliance positions |
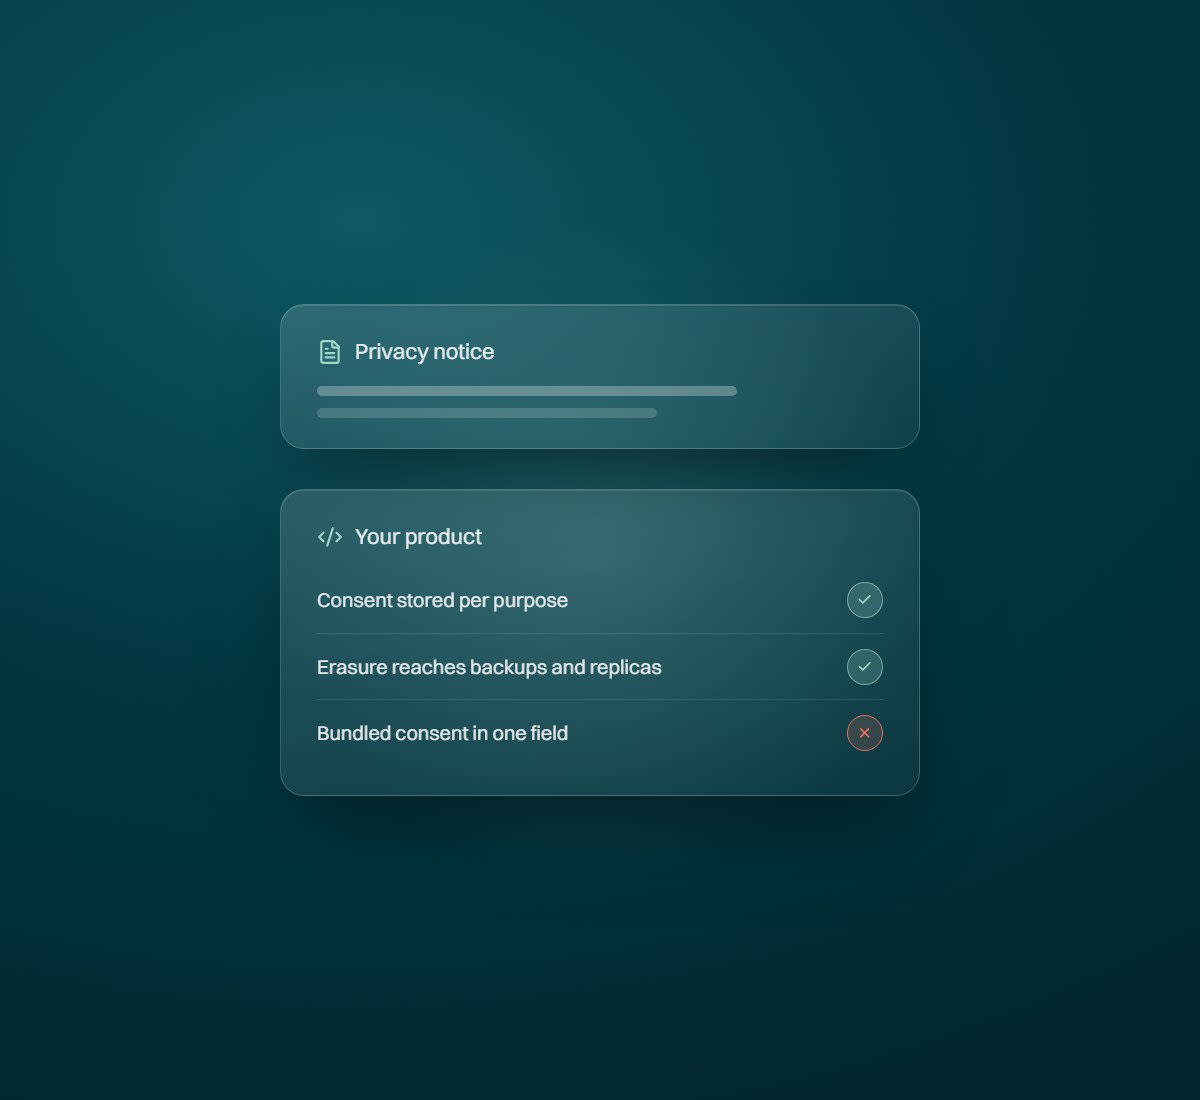
A privacy notice is a promise. Your product is what actually keeps it.
Consent that’s granular in the notice but bundled in the database isn’t compliant consent — it’s a policy document describing a system that doesn’t exist.
A right to erasure only holds up if deletion actually reaches every backup, replica, and downstream analytics table it was copied to.
Cross-border transfer restrictions apply the moment data leaves the country, whether or not your architecture diagram was built with that boundary in mind.
Regulators, auditors, and enterprise customers are increasingly asking to see the system, not just the policy.
How a DPDP readiness review runs, step by step
Data mapping
We inventory what personal data you collect, why, where it flows, and who can access it — the foundation every other obligation depends on.
Gap assessment
We compare your current consent, rights-handling, and breach-response processes against the Act and the DPDP Rules, 2025 and flag exactly where product and engineering changes are needed.
Design & build
We design and implement the consent flows, rights-request systems, and retention automation needed to close the gaps identified — working alongside your engineering team.
Documentation & handover
You leave with working systems and the documentation — data maps, DPIAs, response runbooks — needed to demonstrate compliance to auditors, partners, or the Board.
Who runs your DPDP readiness review
The controls the DPDP Rules, 2025 ask for, such as consent records, security safeguards and logs, are ones we have already built into regulated banking software. In that digital KYC project:
- Consent
- Every onboarding verified identity against an Officially Valid Document and captured the customer's consent.
- Data location
- Customer data stays in the bank's own India-region infrastructure.
- Data minimisation
- Aadhaar numbers are masked before storage, and documents are encrypted at rest (AES-256) and in transit (TLS 1.3).
- Access control
- Role-based access with maker-checker approval, keys managed in AWS KMS, and VAPT before go-live.
- Audit trail
- Every onboarding step writes to an immutable audit log. The bank's first internal audit after launch closed with zero observations on digital KYC.
Reviews are run by Tizora's data protection team. We have handled regulated personal data in projects such as our digital KYC platform for a regional bank.

DPDP vs GDPR: what changes if you already comply with GDPR
| Topic | GDPR | DPDP Act and Rules |
|---|---|---|
| Legal basis for processing | Six lawful bases, including legitimate interests | Consent, or a limited list of specified legitimate uses; no general legitimate-interests basis |
| Consent Managers | No equivalent | Registered, India-based Consent Managers that let people manage consent across services |
| Breach notification | To the supervisory authority within 72 hours where there is a risk to individuals | To the Board and each affected Data Principal without delay, with a detailed Board report within 72 hours |
| Children | Age of consent set by each member state, between 13 and 16 | Under 18; verifiable parental consent required |
| Transfers abroad | Only with safeguards such as adequacy decisions or standard contractual clauses | Allowed unless the government restricts a country |
| Maximum penalty | €20 million or 4% of global annual turnover | Up to ₹ 250 crore per breach |
FAQ
DPDP compliance services FAQs
DPDP compliance in India means meeting the Digital Personal Data Protection Act, 2023 and the DPDP Rules, 2025 in how your product collects, uses, stores and deletes personal data. It covers clear notice and consent, Data Principal rights, security safeguards, retention limits and reporting breaches to the Data Protection Board. Most duties apply from 13 May 2027.
A DPDP compliance checklist should cover data mapping, an itemized notice and consent records, flows for access, correction, erasure and nomination, a grievance contact that replies within 90 days, deletion when a purpose ends, security safeguards with logs kept for at least one year, and breach reporting to the Board within 72 hours. The checklist on this page lists all 12 items.
The DPDP Rules, 2025 were notified on 13 November 2025 and apply in phases. Rules for the Data Protection Board took effect immediately, Consent Manager rules take effect on 13 November 2026, and most duties for Data Fiduciaries, including notice, security safeguards, breach intimation, retention and Data Principal rights, take effect on 13 May 2027.
The Data Protection Board can impose penalties of up to ₹ 250 crore for failing to take reasonable security safeguards, up to ₹ 200 crore for failing to notify a personal data breach or for breaching obligations on children's data, and up to ₹ 50 crore for other violations.
No. Consent Managers are companies based in India that are registered with the Data Protection Board. Tizora designs and builds the consent flows and consent records inside your own product, and can design them to work with a registered Consent Manager.
Yes, if you process the personal data of individuals located in India in connection with offering goods or services to them. Location of incorporation doesn’t exempt an organization — what matters is whose data is being processed and in what context.
The government designates certain Data Fiduciaries as "Significant" based on factors like volume and sensitivity of data processed, and risk to the rights of Data Principals. That designation brings additional obligations — appointing a Data Protection Officer based in India, independent data audits, and data protection impact assessments. We help you assess where you currently stand and prepare for that tier if it’s a realistic trajectory.
There’s meaningful overlap in principles — consent, purpose limitation, data subject rights — but the DPDP Act has its own specific mechanics: a narrower, more consent-centric legal basis structure, a "Consent Manager" concept unique to the Indian framework, and different breach-notification and cross-border-transfer rules. Existing GDPR infrastructure is a strong starting point, not a substitute.
DPDP compliance software, such as a consent management platform, can help, but it does not make a product compliant on its own. Consent, rights requests, deletion and breach reporting have to work inside your own systems and data. Tizora builds those controls into your product and can connect them to a consent tool or a registered Consent Manager if you use one.
Under Rule 7 of the DPDP Rules, you must inform each affected Data Principal and the Data Protection Board without delay, and send the Board a detailed report within 72 hours of becoming aware of the breach. The practical challenge is almost always detection and internal escalation speed, which is why we focus on the instrumentation and runbooks that get a breach identified and reported in time.
Our focus is the product and engineering work — consent flows, data architecture, rights fulfillment, breach response systems — that most compliance programs underinvest in. We work alongside your legal counsel or DPO rather than replacing them, and can support with the technical documentation they need.
Can't find what you're looking for? Reach out to our engineering team directly.
Find out where your product actually stands.
A DPDP readiness review maps your real data flows against the Act and the DPDP Rules, 2025, with time to build what is missing before 13 May 2027. The DPDP compliance checklist above shows what to build. The review shows which items your product already meets and which it does not.
