Security that ships with the code, not after it.
Application security services built into your SDLC
Most breaches don’t start with a zero-day — they start with a broken access control check, an unpatched dependency, or a misconfigured cloud bucket that shipped because no one was looking for it. We build application security into your SDLC so those gaps get caught in code review, not in an incident report.
Tizora's application security services find and fix vulnerabilities in web applications and APIs through manual code review, penetration testing and automated scanning in your CI pipeline. Every finding is manually verified against the OWASP Top 10:2025 and ASVS 5.0, then re-tested after it is fixed.
What our application security services cover
Application security testing that mirrors how software actually gets built
Vulnerability scan vs penetration test vs secure code review
| Question | Vulnerability scan | Penetration test | Secure code review |
|---|---|---|---|
| How it works | Automated tools flag known vulnerability signatures | A tester attacks the running application and APIs like a real attacker | A reviewer reads authentication, authorization, session and data-access code line by line |
| Best at | Fast, broad coverage of known issues | Chained findings and proving what is actually exploitable | Logic and authorization flaws that need an understanding of intent |
| Misses | Business-logic flaws; produces false positives | Code paths it never reaches | Runtime and configuration issues |
| When to use | Continuously, in CI on every pull request | At major releases, or at least annually | For new features and high-risk code |
Secure SDLC: secure by default, not secure by exception
The cheapest vulnerability to fix is the one that never ships. We work with engineering teams to move security decisions earlier, so fewer findings surface after the fact.
Threat modeling at design time
New features get a lightweight threat model before implementation, so authorization boundaries and trust assumptions are explicit from day one.
SAST & SCA in CI
Static analysis and dependency scanning run on every pull request, catching known vulnerability classes before they merge — not at the next quarterly audit.
Secrets & configuration hygiene
No credentials in source control, no default configurations in production — enforced through tooling, not a policy document no one reads.
Incident-ready logging
Authentication events, authorization failures, and administrative actions are logged in a form that actually supports investigation, not just uptime monitoring.
Mapped to the OWASP Top 10:2025 and API Security Top 10
Every engagement is mapped to the OWASP Top 10:2025, with API security testing against the OWASP API Security Top 10 (2023) and infrastructure risks the standard list doesn’t fully capture. LLM features and AI agents need their own AI security assessment.
Application layer
- Broken access control (A01)
- Injection, SQL, NoSQL and command (A05)
- Authentication failures (A07)
- Insecure design and business logic (A06)
- Cryptographic failures (A04)
- Mishandling of exceptional conditions (A10)
Application layer
Where most exploited flaws start: broken access control, injection, authentication failures, insecure design and business logic, cryptographic failures, and mishandling of exceptional conditions.
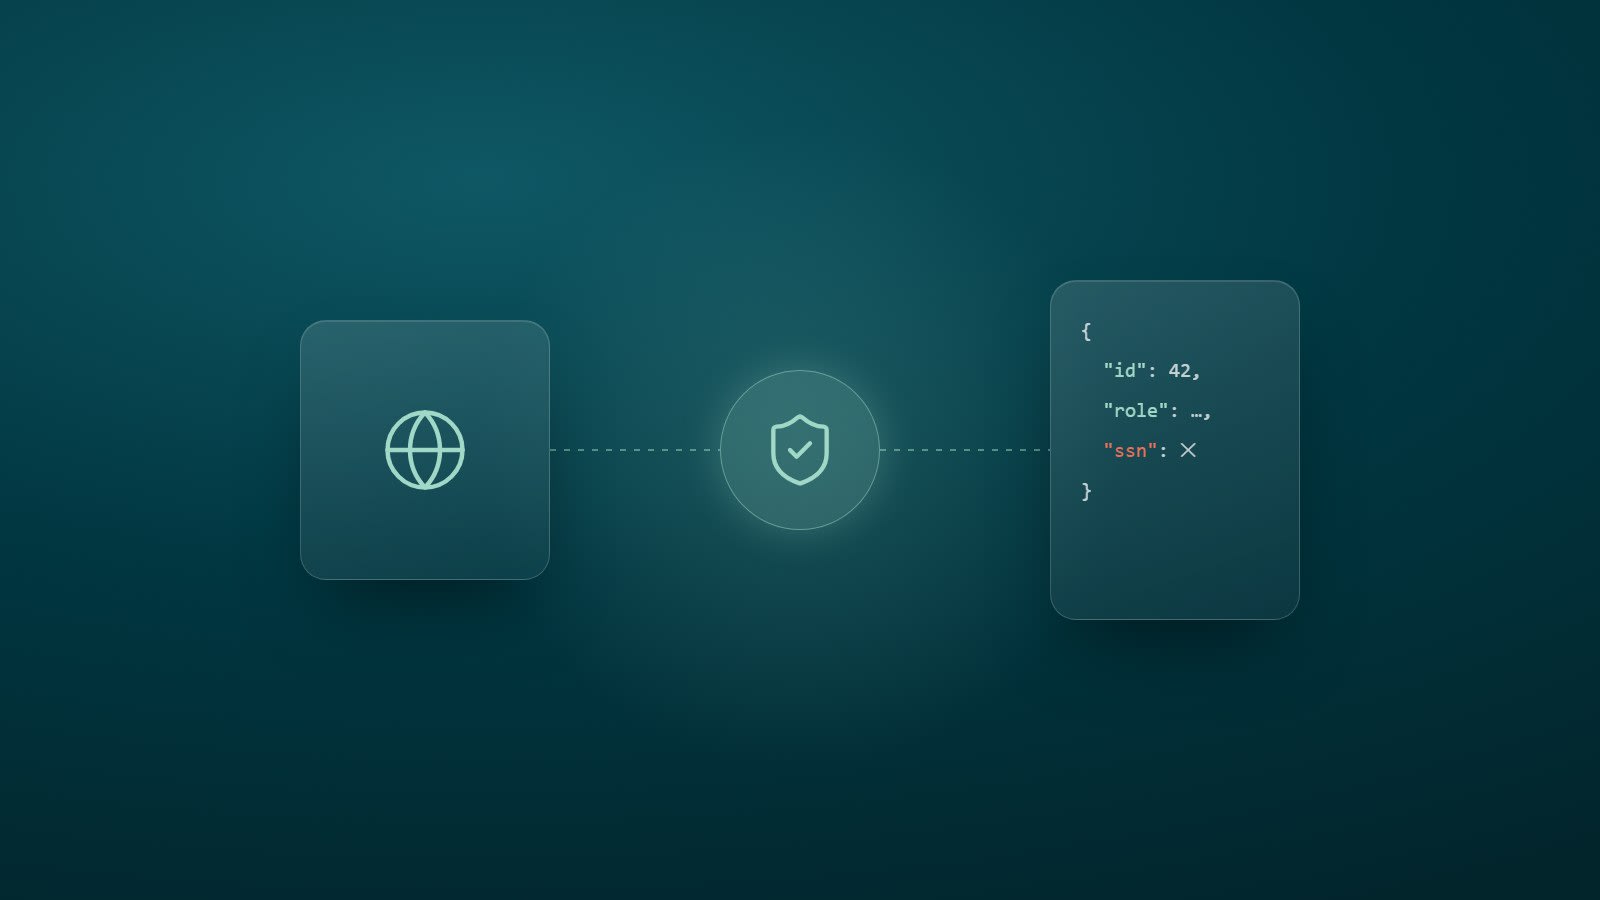
API and integration layer
- Broken object and function level authorization (API1, API5)
- Broken object property level authorization, including excessive data exposure (API3)
- Server-side request forgery (API7)
- Unrestricted resource consumption (API4)
API and integration layer
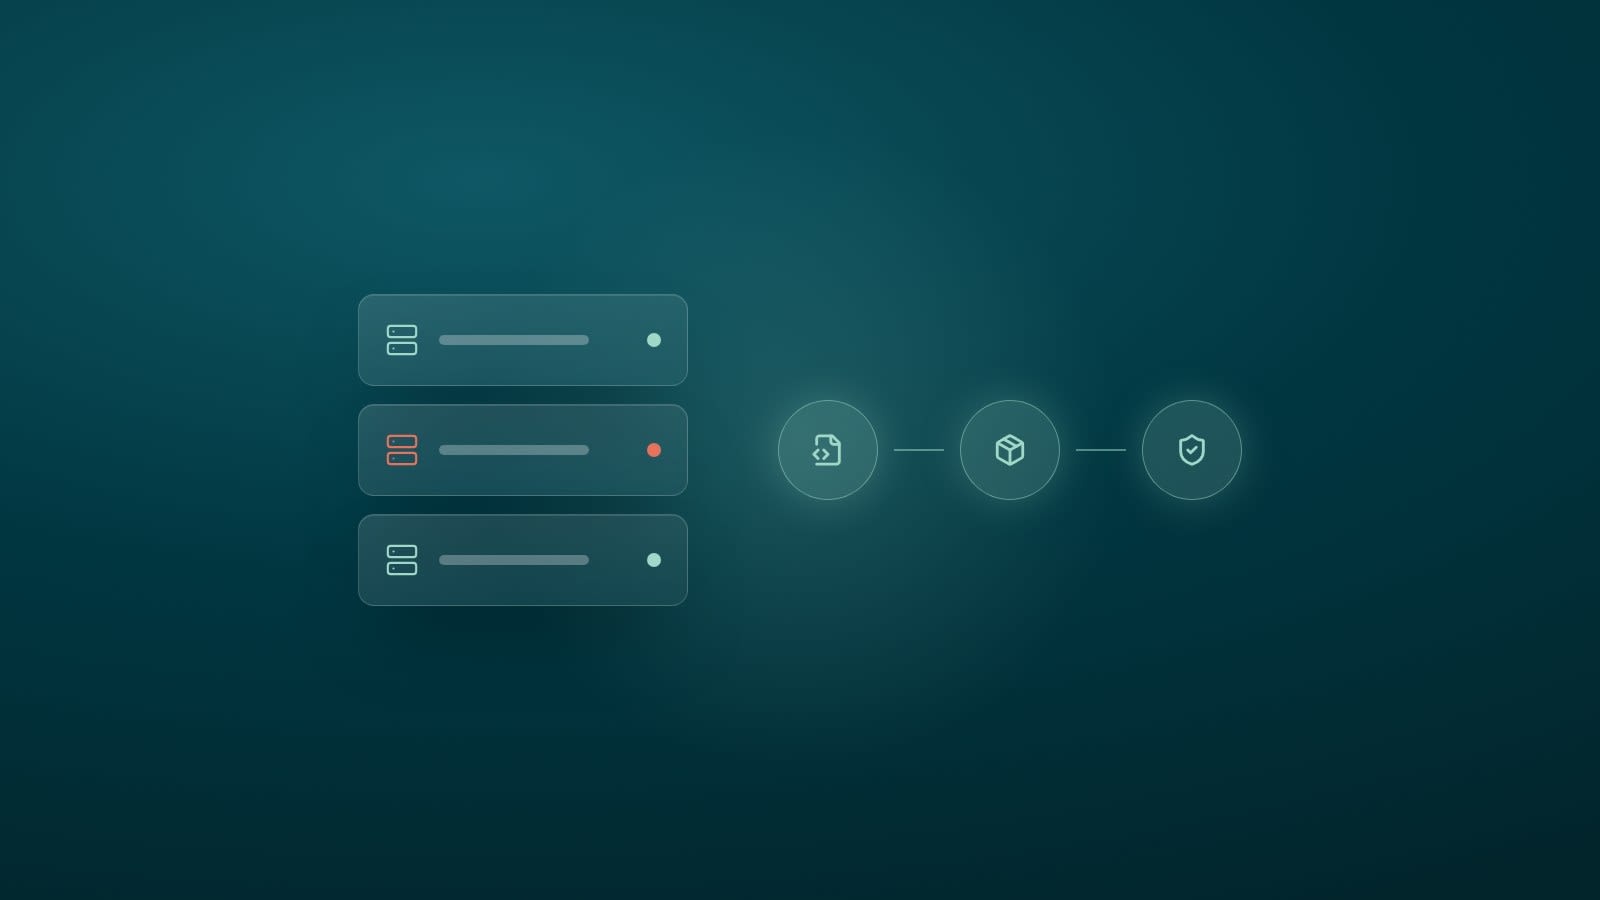
How your services talk to each other: object, function and property level authorization, server-side request forgery, and unrestricted resource consumption.
Infrastructure and pipeline
- Security misconfiguration (A02)
- Software supply chain failures (A03)
- Software or data integrity failures in CI/CD and builds (A08)
- Security logging and alerting failures (A09)
Infrastructure and pipeline
What ships and runs the code: security misconfiguration, software supply chain failures, software or data integrity failures in CI/CD and builds, and security logging and alerting failures.
The vulnerabilities that actually get exploited are rarely the exotic ones.
They’re the access-control check that works for one role and not another, shipped by a team that never had a security engineer look at the design before it went out.
How an application security assessment runs, step by step
Scoping & threat modeling
We map the application’s attack surface, trust boundaries, and highest-value assets before testing begins, so effort goes where the real risk is.
Automated & manual testing
SAST, DAST, and SCA scans run alongside manual code review and hands-on penetration testing against the live application and its APIs.
Verified findings & impact
Every finding is manually verified and rated by real exploitability and business impact — no unconfirmed scanner noise in the final report.
Remediation & re-test
We work directly with engineers to fix confirmed issues, then re-test to verify closure before the engagement is marked complete.
What you get from our application security services
Every verified finding in the report follows the same structure, so engineers can act on it without re-triaging.
Finding
A short, plain title for the issue.
OWASP category
The OWASP Top 10:2025 or API Security Top 10 entry it maps to, such as A01:2025 Broken Access Control.
Layer
Where it lives: application, API or infrastructure.
Severity and exploitability
How serious the issue is and who could exploit it.
How it was verified
A short reproduction showing the issue is real.
Fix
The code or configuration change we recommend.
Re-test
Whether the issue is closed or still open after we re-test.
FAQ
Application security services FAQs
Application security services find and fix vulnerabilities in web applications and APIs. Tizora's services combine manual secure code review, penetration testing and automated scanning in your CI pipeline, with every finding manually verified, fixed with your engineers and re-tested.
Every assessment is structured against the OWASP Top 10:2025 and the OWASP Application Security Verification Standard (ASVS) 5.0, with APIs tested against the OWASP API Security Top 10.
SAST analyzes source code without running it, DAST tests the running application from the outside, and SCA checks third-party and open-source components for known vulnerabilities. We run all three and cross-check them with manual review, because none of them reliably finds business-logic or authorization flaws.
A scan is automated and flags known vulnerability signatures — it’s fast and broad but generates false positives and misses business-logic flaws entirely. A penetration test adds a human who thinks like an attacker: chaining low-severity issues together, testing authorization boundaries a scanner can’t reason about, and confirming what’s actually exploitable. We use both — automation for coverage, manual testing for the findings that matter.
We strongly prefer a staging or dedicated test environment that mirrors production, to avoid any risk of disruption. Where production testing is required — for issues that only reproduce there — we scope it carefully with rate limits and a rollback plan agreed in advance.
Every automated finding is manually verified before it makes it into the report. If we can’t reproduce a real impact, it doesn’t get listed as a vulnerability — it gets noted separately as informational, if at all. You get a report you can act on, not one you have to triage yourself.
Yes. We commonly wire SAST and dependency scanning directly into your pull-request checks, so known vulnerability classes are caught before merge rather than in a periodic audit months later.
For most teams shipping regularly, we recommend a full assessment at major release milestones or at least annually, with continuous automated scanning in between. Applications handling sensitive data or operating in regulated industries often warrant more frequent manual review.
Can't find what you're looking for? Reach out to our engineering team directly.
Know where your application actually stands.
From a single focused penetration test to full SDLC integration, we’ll help you find and fix what matters before it becomes an incident report.
