Cybersecurity services for AI, apps and Shopify
Security testing for the software you ship: LLM applications and agents, web applications and APIs, and Shopify apps connected to many stores. Each service below links to its full scope.
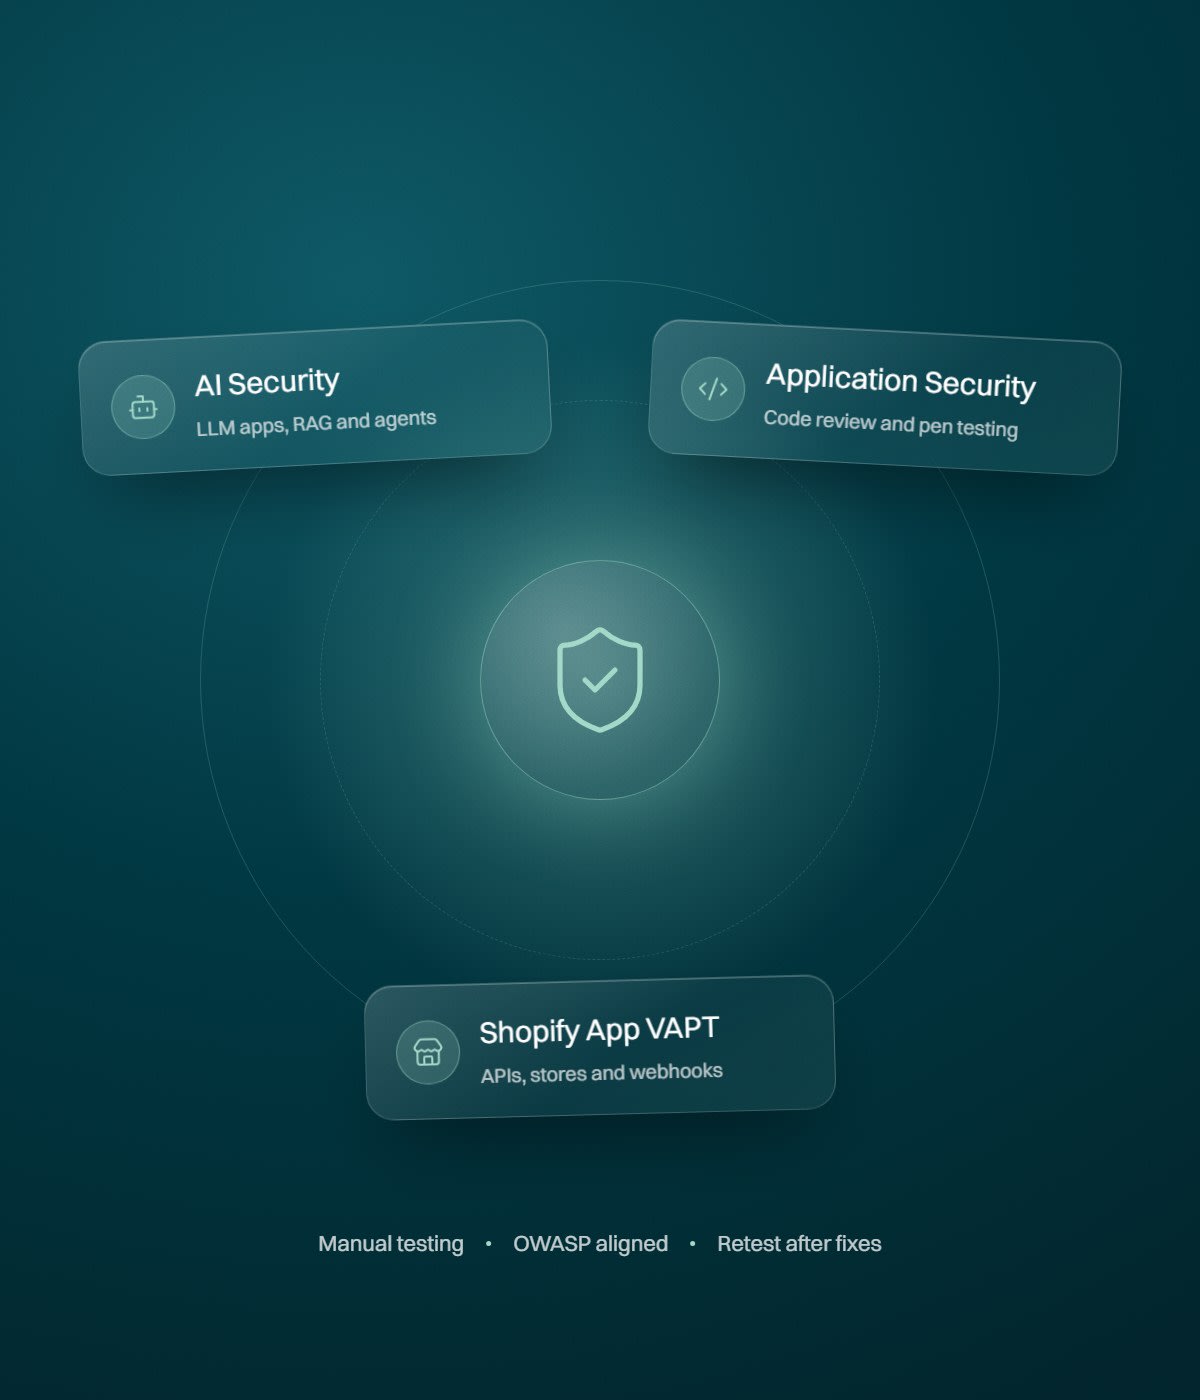
Tizora's cybersecurity services cover three areas: AI security for LLM applications, RAG pipelines and agents; application security built into the software development lifecycle; and VAPT for Shopify apps. Automated scanning is paired with manual testing, and findings come with remediation guidance and a retest.
AI Security
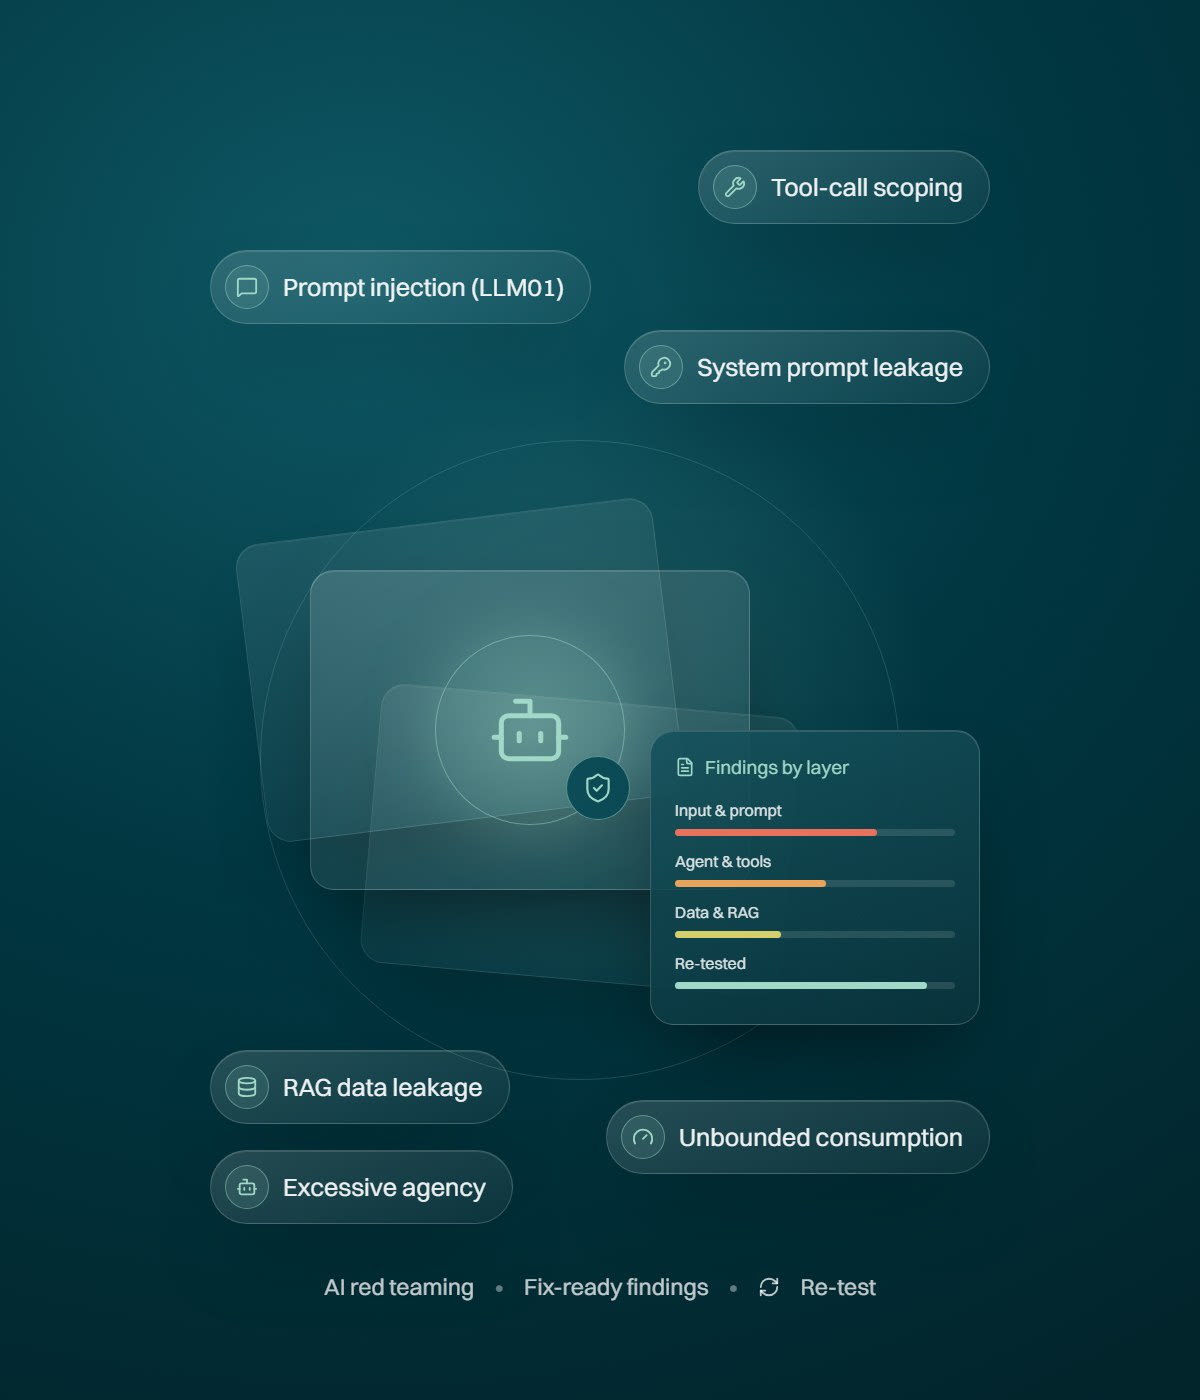
AI security assessment for LLM apps, RAG pipelines and AI agents: OWASP LLM Top 10 red teaming, fix-ready findings and a re-test to confirm closure.
What it covers
- LLM red-teaming
- RAG & agent security
- Guardrail design
- Model risk assessment
Application Security Services
Application security services: manual code review, pentesting and CI scanning mapped to OWASP Top 10:2025, with every finding verified and re-tested.
What it covers
- Secure code review
- Penetration testing
- Threat modeling
- DevSecOps integration
Shopify App VAPT
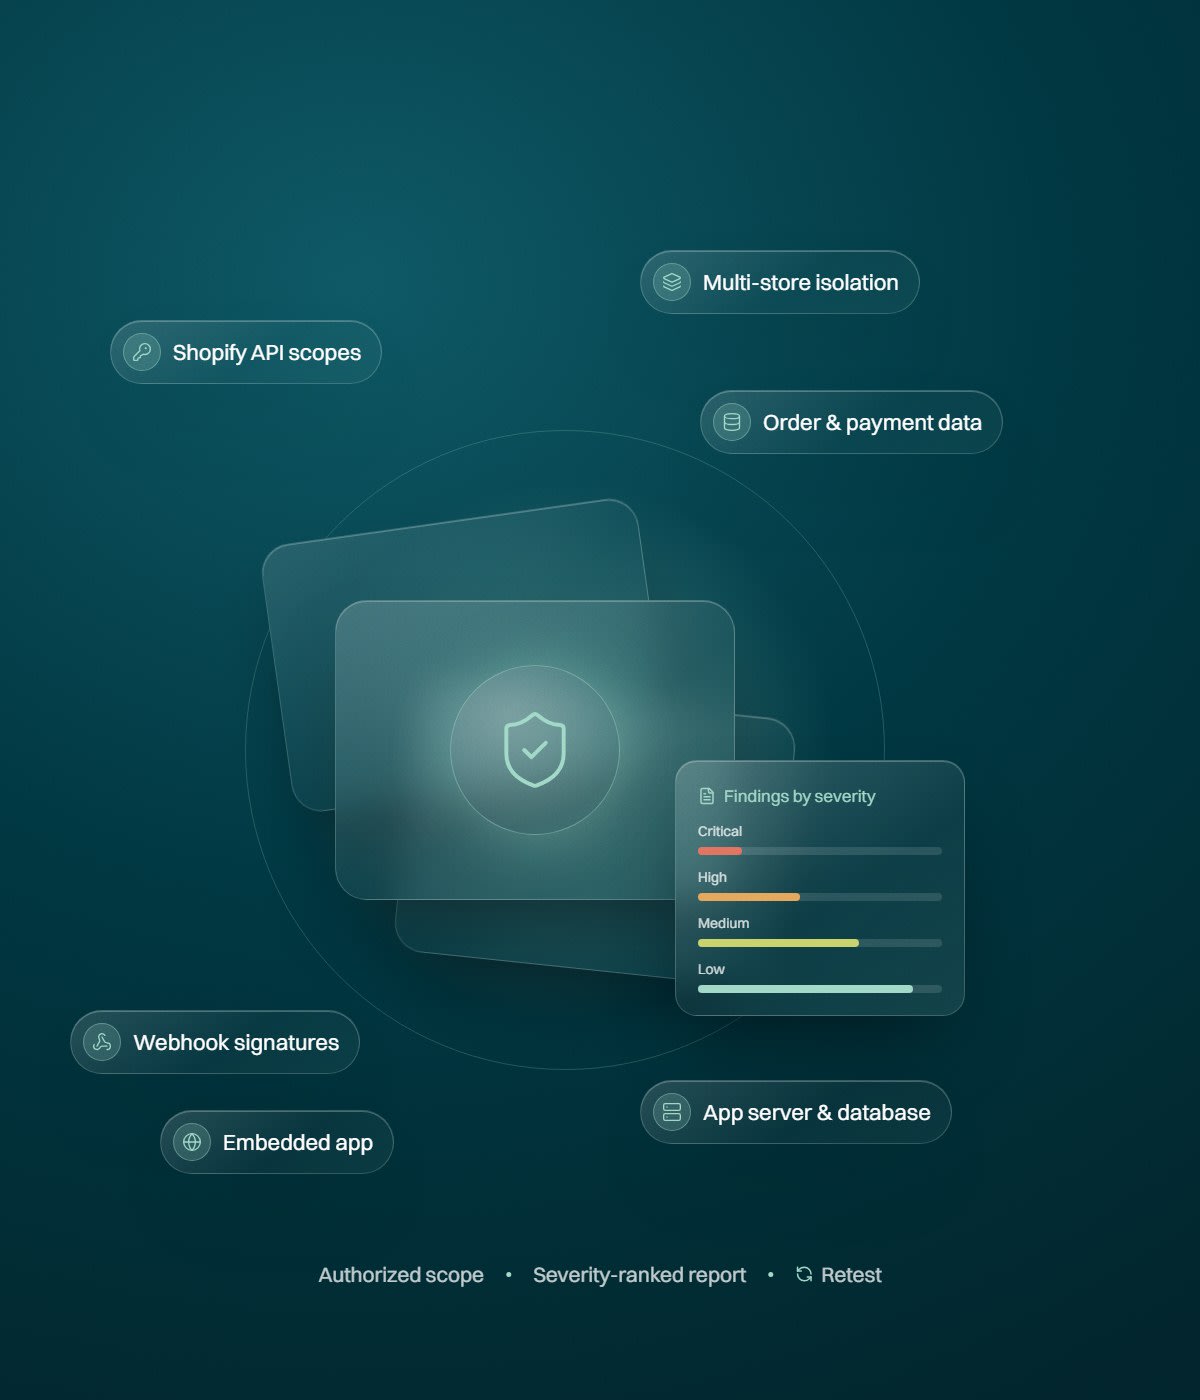
Shopify app VAPT from Tizora: we test Shopify API access, multi-store isolation, webhooks, order and customer data, and payment integrations, then retest fixes.
What it covers
- Shopify API security
- Order, customer and transaction data
- Multi-store security
- Webhooks and event processing
How we work
What every cybersecurity engagement includes
The same ground rules apply whether we are testing an AI agent, a web application or a Shopify app.
Manual testing, not just scanners
Automated findings are verified by hand, and testers look for the business-logic and model-layer flaws that scanners miss.
Mapped to recognised standards
Findings map to the OWASP Top 10, the OWASP ASVS and the OWASP Top 10 for LLM Applications.
Fix-ready findings
Each finding comes with severity, evidence and concrete engineering fixes, not just a score.
Retest to confirm
After your team fixes the issues, we retest to confirm they are closed.
FAQ
Cybersecurity services FAQs
Three services: AI security for LLM applications, RAG pipelines and agents; application security across the software development lifecycle, including secure code review and penetration testing; and VAPT for Shopify apps and their connected stores.
A traditional web application has a fixed set of inputs and predictable code paths. An LLM feature accepts open-ended natural language, often from untrusted users, and turns it into decisions, queries or tool calls, so it can be attacked through the conversation itself with prompt injection, data leakage and agent abuse.
A Shopify app VAPT (vulnerability assessment and penetration testing) is authorized security testing of a Shopify app and its integrations: Shopify API access and scopes, multi-store data isolation, webhooks, the app server and database, the embedded app and any payment integrations, with a report of findings ranked by severity.
No. Scanners flag known patterns but miss business-logic and authorization flaws. Every automated finding is manually verified, and manual testing covers the paths an attacker would actually use.
A written report with each finding, its severity, evidence and remediation steps, followed by engineering support where agreed and a retest to confirm the fixes.
Find the gap before it is an incident
Tell us what you are shipping, an AI feature, a web application or a Shopify app, and we will suggest the right assessment.
